Event · Presentation
Third-Party Risk Management: How to apply due diligence to supply chain control.
A practical, multidisciplinary guide coordinated by Carlos Alberto Saiz Peña with more than a dozen experts in compliance, cybersecurity, privacy and AI.
- 28 September 2026
- 19:00h - 21:00h
- ICAM — Madrid Bar AssociationC/ Serrano 9. Assembly Hall (first floor). 28001 Madrid
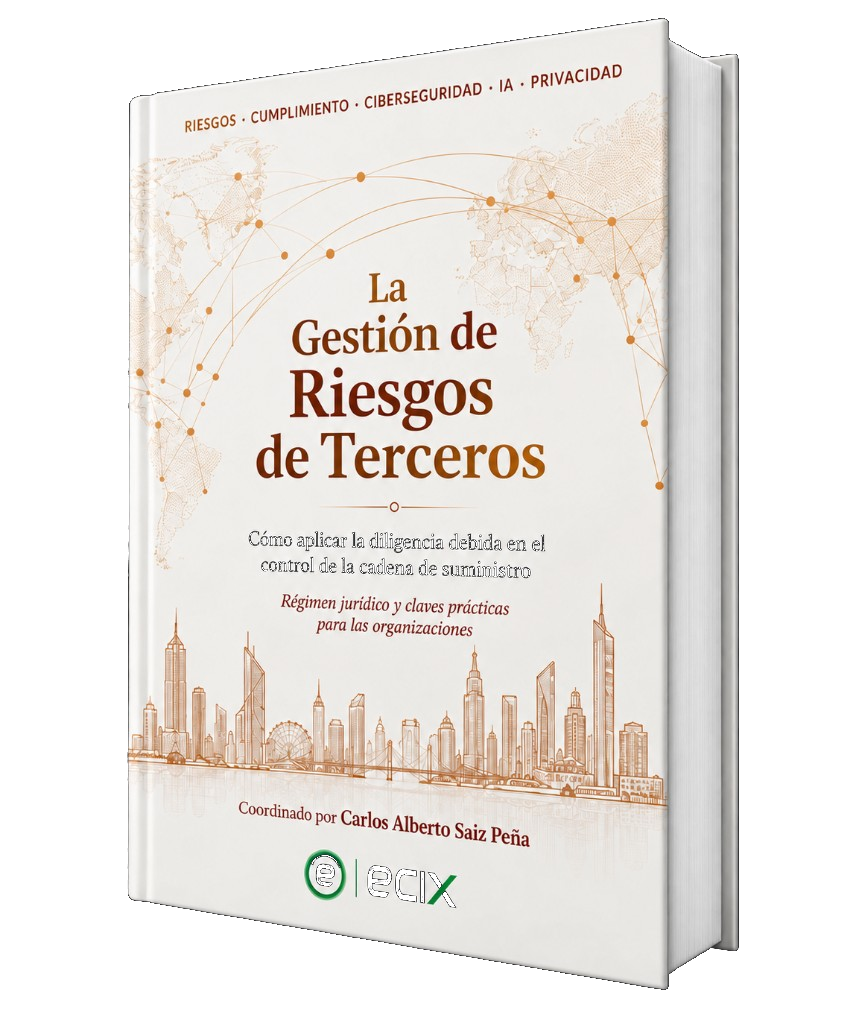
 Available on Amazon
About the book
A guide to governing the risk that enters through every link.
This work offers a practical, multidisciplinary guide to identify, assess and monitor legal, reputational and cybersecurity risks against requirements such as GDPR, NIS2, DORA and AI regulation.
- GDPR
- NIS2
- DORA
- AI regulation
The context
The regulatory and operational challenge
Suppliers, subcontractors and business partners now form an extensive and complex value chain. An error in any link creates legal, reputational and operational risks that the organisation ultimately assumes. Due diligence on third parties is a central compliance obligation.
Value proposition
From the risk map to actionable decisions.
A work designed to turn regulatory complexity into a clear, efficient and shared working model.
Multidisciplinary vision
Risk, AI, Cybersecurity and Legal connected in a single reading.
Applicable criteria
Clear criteria and methodologies that can be put into practice from day one.
Scale and efficiency
Efficient models to manage extensive supplier chains.
Target audience
For those who protect the value chain.
A shared perspective for roles that need to coordinate on third-party risk.
- Compliance Officers and Legal Directors
- CISOs and Cybersecurity Leaders
- Data Protection Officers (DPO)
- Procurement and Innovation Directors
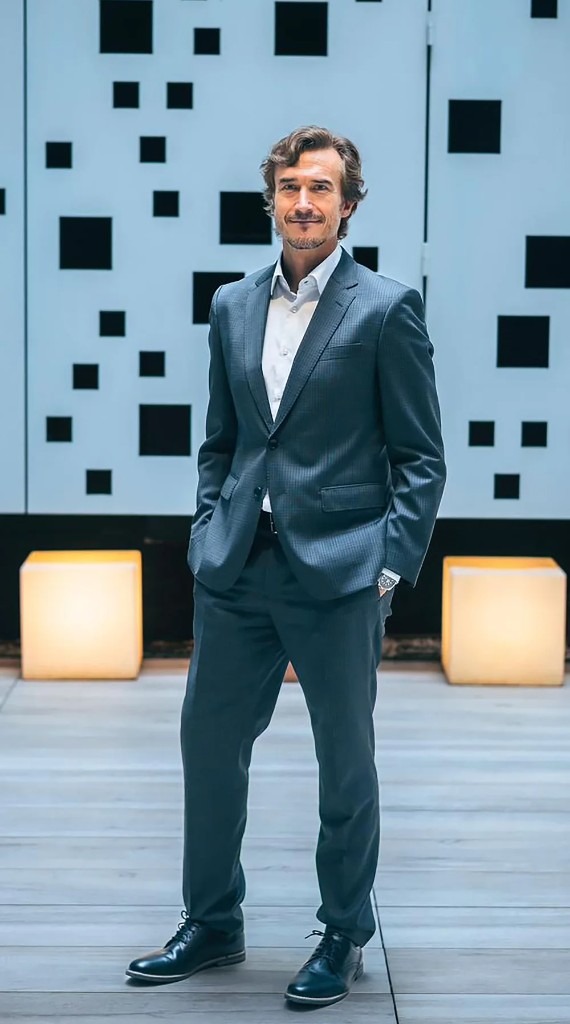
Work direction
Carlos Alberto Saiz Peña
Coordinator of the work and lead participant in the presentation
Vice President and Partner of Risk & Compliance at ECIX Tech
Partner and Vice President of ECIX Group, Carlos Alberto Saiz Peña has 25 years of experience in Privacy, Cybersecurity, Risk Management, Compliance and Legaltech. He is Vice President of CUMPLEN, ISMS Forum Spain and ENATIC, Director of the Data Privacy Institute and a member of specialised Artificial Intelligence groups and observatories. He has studied at MIT and ESADE and has been recognised for 13 consecutive years by Best Lawyers in Privacy and Technology in Spain.
“This work brings together the practical experience of top-tier professionals to offer a real toolbox that helps build, improve or strengthen the third-party risk management model.”
Carlos Alberto on LinkedInBook presentation
Session on 28 September.
19:00 — 21:00
ICAM — Madrid Bar Association
C/ Serrano 9. Assembly Hall (first floor). 28001 Madrid
In person · by invitation
Session programme
- Welcome
- Book presentation and speaker interventions
Presentation by Mabel Klimt.
5th Deputy of the Madrid Bar Association. Head of Technology, Digitalisation and Culture.
Interventions
- Miguel Soler Ruiz-BoadaGeneral Counsel. Compliance Director & Deputy Company Secretary PROSEGUR.
- Francisco Pérez-BesDeputy of the Spanish Data Protection Agency (AEPD).
- Eloy VelascoJudge and Magistrate, former member of the National Court.
Acknowledgements and closing by Carlos Alberto Saiz Peña, coordinator of the work.
- Cocktail and Networking (Library Courtyard)
More information:
comunicacion@ecix.tech